Enterprise Cybersecurity & Application Hardening: The Complete Engineering Guide
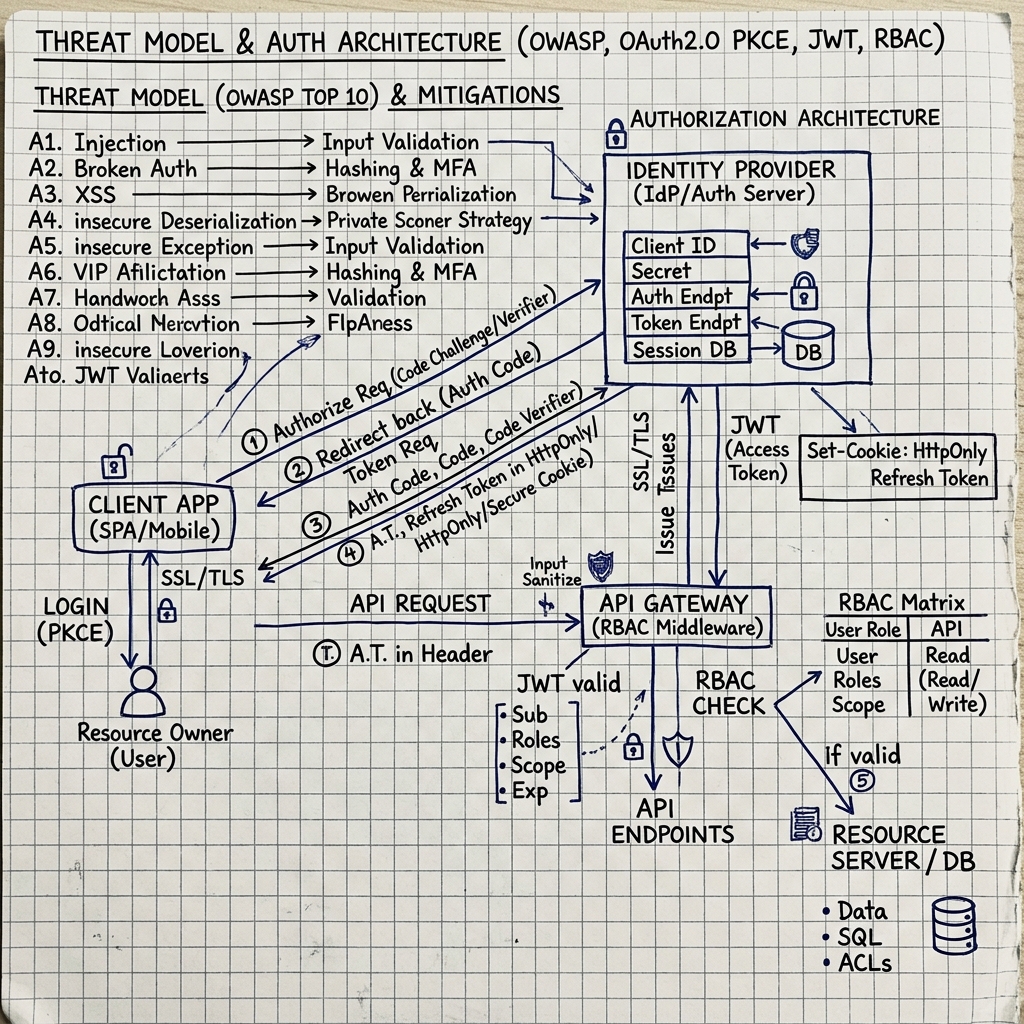
A comprehensive 5,000+ word technical guide covering OWASP Top 10 mitigations, zero-trust JWT/OAuth auth pipelines, BOLA RBAC guards, Docker/Kubernetes container security, and SOC 2 / ISO 27001 compliance.
Enterprise Cybersecurity & Application Hardening Guide by Rohit Sharma
Cybersecurity is no longer an optional add-on at the conclusion of software development—it is the very foundation of modern cloud architecture. As Rohit Sharma, Product Manager and Senior Software Lead, notes: "A single un-mitigated API vulnerability or data breach can destroy years of customer trust and brand reputation."
---
SECTION 1: OWASP TOP 10 MITIGATION BLUEPRINT
The Open Web Application Security Project (OWASP) Top 10 represents the most critical security risks facing web applications today.
#### 1.1 Broken Object Level Authorization (BOLA / IDOR)
```typescript
// Secure BOLA Guard in Node.js / Prisma ORM
export async function getOrderById(orderId: string, currentUserId: string) {
const order = await prisma.order.findFirst({
where: {
id: orderId,
userId: currentUserId, // Explicit ownership verification
},
});
if (!order) {
throw new UnauthorizedError('Order not found or access denied');
}
return order;
}
```
#### 1.2 Injection Flaws (SQL, NoSQL & Command Injection)
#### 1.3 Cross-Site Scripting (XSS) & Content Security Policy (CSP)
---
SECTION 2: ZERO-TRUST AUTHENTICATION & AUTHORIZATION PIPELINES
Architecting resilient authentication requires short-lived credentials, multi-factor verification, and strict session management.
#### 2.1 Dual Token JWT Architecture (Access + Refresh Tokens)
#### 2.2 Multi-Factor Authentication (MFA / TOTP)
---
SECTION 3: CLOUD CONTAINER & DEVOPS SECURITY
Hardening infrastructure requires securing Docker containers, Kubernetes pods, and CI/CD deployment pipelines.
#### 3.1 Docker Non-Root Container Execution
```dockerfile
# Multi-Stage Docker Hardening Blueprint
FROM node:20-alpine AS builder
WORKDIR /app
COPY package*.json ./
RUN npm ci --only=production
FROM node:20-alpine AS runner
WORKDIR /app
COPY --from=builder /app/node_modules ./node_modules
COPY . .
USER node
EXPOSE 3000
CMD ["npm", "start"]
```
#### 3.2 Automated CI/CD Dependency Auditing
---
SECTION 4: ENTERPRISE COMPLIANCE (SOC 2, ISO 27001, GDPR)
Enterprise B2B clients demand verified compliance certifications before purchasing software licenses.
#### 4.1 SOC 2 Type II Compliance Controls
---
CONCLUSION & CHECKLIST
Implementing a zero-trust, security-first mindset ensures that web applications, SaaS platforms, and enterprise APIs remain resilient against modern cyber threats.
Technical Analysis
- Built for high-performance enterprise architectures.
- Optimized for Core Web Vitals and SEO visibility.
- Implements industry-standard security protocols.
Written by Rohit Sharma
Full Stack Developer & Technical Architect
Spread the Knowledge
Related Engineering Portfolios & Profiles
Continue Reading
7 Clean Code Principles Every JavaScript Developer Should Know
Write code that humans can read, not just machines. A guide to the Solid principles and clean code practices for modern JS/TS.
How much does it cost to hire a full stack developer in India?
A comprehensive guide on the costs of hiring elite full-stack developers in India. Understand the pricing models, value propositions, and why India remains a top destination for quality software engineering.
Building a SaaS MVP in 30 Days with INDJS Boilerplate
Learn how to leverage the INDJS framework to build a robust, production-ready SaaS MVP in just one month. We cover auth, billing, and deployment.